Broadcom Brings VM API to CNCF Sandbox and Pushes Workload Conformance on VKS
Broadcom's VM API enters the CNCF Sandbox, it co-chairs a new workload conformance group, and 20+ partner tools are validated on VKS.
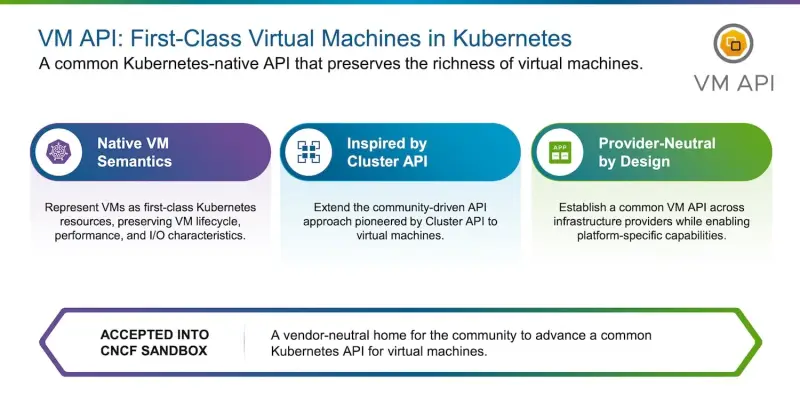
If you run VMs and containers side by side, Broadcom's KubeCon North America 2026 announcements deserve a close read. Three things landed together. Its VM API project has been accepted into the CNCF Sandbox, Broadcom is co-chairing a newly formed Workload Conformance Working Group in the Kubernetes community, and more than 20 partner solutions have been validated to run on VMware vSphere Kubernetes Service (VKS), the Kubernetes runtime inside VMware Cloud Foundation. Read together, they point at one goal: treating a virtual machine as just another Kubernetes object.
What VM API is actually trying to do
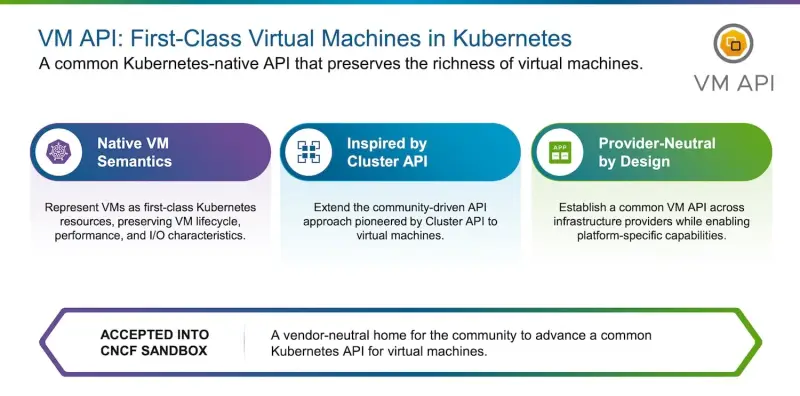
VM API provisions and manages virtual machines through Kubernetes APIs, across multiple heterogeneous infrastructure providers. A VM becomes a first-class Kubernetes resource, sitting next to containers under the same declarative model. That's the pitch, and the design lineage matters here. VM API grows out of Broadcom's VM Operator, which brought Kubernetes-native VM management to the vSphere side of VMware Cloud Foundation. It borrows its shape from Cluster API, the community project that abstracted cluster lifecycle across providers.
Moving the project under CNCF stewardship is meant to give other infrastructure providers a common API and operating model to implement. Workload consistency is supposed to come from conformance rather than from any one vendor's tooling.
Here's the thing: a common API only matters if more than one platform actually speaks it. Cluster API's track record is the precedent Broadcom is pointing to, and that's a fair comparison to draw. But the announcement doesn't name other providers committing to implement VM API, and it doesn't give a timeline for that. My read is that this is a direction the company is setting rather than an interoperability story that's already playing out.
Why the VM question keeps coming back
Broadcom's case leans on the Linux Foundation's 2026 Virtual Machines Report, a survey of 492 practitioners. According to the figures Broadcom cites from that report, VMs still account for 53% of production applications, and most organizations expect that share to hold. The report also found that 34% of organizations growing their VM footprint cite AI and agentic workloads as a reason.
Broadcom's argument is that advanced AI workloads need the strict hardware isolation VMs provide, combined with the agility of containers. VM API, in its framing, is the route to running both under one Kubernetes control plane. Teams in this position typically feel the split most sharply at the operations layer: one set of pipelines, policies and observability for containers, and a separate set of tools and ticket queues for the VMs. Bringing both under one API is an attempt to close that gap, whatever you think of the packaging.
Dilpreet Bindra, senior director of engineering in Broadcom's VMware Cloud Foundation Division, put the goal this way: "By contributing the VM API project to CNCF, we are bringing that enterprise-grade reliability to the Kubernetes community." He framed the aim as making VMs first-class citizens alongside containers. Broadcom also says it is among the top five long-term contributors to CNCF projects.
The conformance gap the working group is targeting
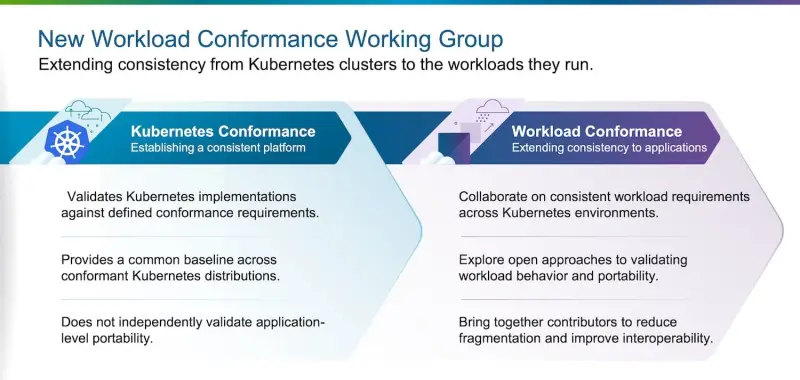
Existing CNCF programs check that a platform exposes the standard Kubernetes APIs, behaves correctly for core container orchestration, and can run AI and machine learning workloads portably. Nothing equivalent exists for the workloads themselves. That's the gap. An independent software vendor that wants to sell into several Kubernetes distributions has to certify against each one separately.
The new working group, which Broadcom co-chairs, aims to set a shared, verifiable standard for how workloads behave on any conformant Kubernetes environment. The stated ideal is that an ISV validates once and deploys everywhere. Broadcom, as VMware, also helped pioneer Sonobuoy, the diagnostic engine behind the CNCF's Certified Kubernetes Conformance Program, so the company has prior form in this area.
The group is brand new, and it hasn't published a standard or a timeline. Matthew Flug, research manager for Intelligent Application Modernization and Deployment Platforms at IDC, said the priority for organizations running both VMs and containers "is applying consistent governance and policy enforcement across both." He added that "conformance with open standards from the CNCF also helps mitigate vendor lock-in concerns as organizations decide how each workload should run." That second point is the one platform teams should hold onto. Workload-level conformance, if it lands, reduces the cost of switching where a workload runs.
The VKS validated partner list
VKS is the CNCF-certified Kubernetes runtime built into VMware Cloud Foundation. It runs directly on the hypervisor, so VMs, containers and AI workloads share the same clusters and one control plane. Broadcom says this removes the separate infrastructure layer a standalone Kubernetes distribution typically needs. Whether that's a saving for you depends on how much of that layer you already run, but the architecture is the selling point.
The new validations fall into six areas, joining an existing catalog that already includes names such as Cribl, Palo Alto Networks, F5, NetApp, Veeam, NVIDIA and Redis:
- Observability: Cisco Splunk, Datadog, Dynatrace, Grafana Labs, and New Relic.
- Security, compliance, and secrets management: CrowdStrike Falcon Platform, HashiCorp Vault, Sysdig Secure, Tigera Lynx, and Wiz.
- Networking, ingress, and service mesh: NetScaler ADC (Citrix), Solo.io (agentgateway, kagent, and Solo Enterprise for Istio), and Traefik Labs.
- Data protection, backup, and storage: Commvault, Dell Technologies PowerProtect Data Manager, HPE Alletra, and Scality RING.
- AI, machine learning, and analytics: Charmed Apache Spark from Canonical, H2O AI Cloud, and SAS Viya.
- Application delivery, databases, and developer platforms: Akuity Argo CD Enterprise and Kargo, KubeDB by AppsCode, Coherent Spark, and Siemens Mendix.
Broadcom's argument for the list is operational. Platform teams pick from a pre-validated catalog and keep the tools they already run as they move from day-one provisioning to day-two operations on VKS. The working group is meant to make that catalog grow without each vendor re-certifying for every platform.
Varun Verma, GVP of Engineering at New Relic, said, "Enterprises running critical workloads on VKS can't afford blind spots. With New Relic now validated on VKS, teams get unified cluster observability, find root causes faster, and tie operational performance directly to business impact."
Broadcom also pointed to Notruf Niederösterreich, which runs a 24×7 emergency response center with a small IT team, as a VKS customer. Alexander Hopfgartner, Chief Technology Officer at Notruf Niederösterreich, said, "VMware vSphere Kubernetes (VKS) Service lets us spin up encapsulated environments and scale horizontally within hours of a major incident, without being locked into specific hardware. That flexibility is critical when lives depend on our systems staying available."
Alongside the partner news, Broadcom highlighted Velero 1.19 with block-level data movement, the Container Object Storage Interface (COSI) moving toward beta with a vSphere COSI driver, and Agent Substrate, a CNCF Sandbox initiative for running agents.
What to check before you plan around this
If you're evaluating VKS, start with the inventory, not the announcement. Map your current observability, security, backup and data services against the validated lists above. Where a tool you depend on is missing, that's a question for the vendor, not an assumption you should make. The source doesn't spell out which versions of each partner product were validated, so confirm that directly before you schedule a migration window.
For the VM API and workload conformance work, the realistic expectation is a long runway. The project has just entered the Sandbox, and the working group has no published standard yet. Watch for the first concrete outputs from the group and for other infrastructure providers saying they'll implement the API. Those two signals will tell you far more than the conference messaging.
Reference links: VM API on GitHub and VMware vSphere Kubernetes Service.


