Entra's memberOf Retirement: MemberOf Next and Transitive Reports To
Entra's memberOf rule operator is being retired, with a grace period for Governance customers. Here's what MemberOf Next and Transitive Reports To change for dynamic groups.
If you run dynamic groups in Microsoft Entra ID, the memberOf rule operator has a retirement date you need on your calendar. Microsoft deprecated it on November 3, 2026, ending its public preview. Customers with Microsoft Entra ID Governance get a grace period, and they can keep their existing configurations until March 31, 2027. Everyone else needs a plan sooner.
The timing is awkward but not accidental. Microsoft has introduced MemberOf Next, a new version of the same capability, now in public preview after its debut at Microsoft Ignite. It ships alongside Transitive Reports To, a new operator that pulls in everyone across a manager's full reporting chain, not just direct reports. My read is that the two together are meant to replace the old operator's use cases, so the migration work is less about rewriting rules and more about changing how and when membership gets evaluated.
Why the original operator is going away
The legacy memberOf operator let administrators build a dynamic rule from the members of existing groups instead of from individual user or device attributes. In practice, that made it the easy way to consolidate members from several groups into one dynamic group, especially where nested group membership wasn't supported.
It never left public preview. Microsoft found that a single memberOf-based rule could slow dynamic membership processing across the whole tenant. That's the core problem the retirement addresses. A rule that drags down every other dynamic group in the tenant is hard to justify in production, and the operator's shared processing model was the root cause.
How MemberOf Next handles membership differently
MemberOf Next moves the work onto a dedicated processing architecture with a fixed schedule. Membership updates run twice a day. Because that workload is kept separate from other dynamic groups, a heavy memberOf-style rule shouldn't stall evaluation for the rest of the tenant. Microsoft says the redesign also lets Entra support larger tenants.
There's a behavioural change to understand here. Entra flattens the membership of the selected source groups. It adds the actual users or devices from those groups to the target group, rather than adding the source groups themselves as members. The end result looks similar on screen, but the target group's membership is a flat list of individuals and devices.
The considerations that will bite if you skip them
Before you touch a single group, go through these constraints. Several of them change how you'd design the group.
- Standard priority is mandatory. MemberOf Next rules are evaluated twice a day, and only groups set to Standard priority are included in that schedule. Groups left at other priorities won't have their membership processed or updated.
- The syntax stays the same. The operator name and rule syntax are retained. Eligible groups can move over by switching priority to Standard, without rewriting rules.
- Source groups must use assigned membership. Dynamic membership groups can't serve as sources. Each rule supports up to 50 source groups.
- Users and devices are supported, with limits. For users, security and Microsoft 365 groups work. For devices, only security groups are supported.
- You can combine conditions. MemberOf can sit alongside other supported rule conditions in one rule, which allows narrower membership logic.
- Duplicates collapse. A user or device that belongs to several source groups appears only once in the target group.
- Only direct members count. Members of nested groups inside a source group aren't included.
- There's a tenant-wide cap. During public preview, a maximum of 1,000 groups and administrative units can use MemberOf Next and Transitive Reports To combined. That count sits inside the overall 15,000 dynamic membership group limit.
- Updates aren't immediate. Because changes apply twice a day, don't use MemberOf Next for access that has to be granted or revoked right away.
- Deleted source groups pause the target. If a source group is deleted, updates to the target group stop. Entra retries at each scheduled run until the issue is fixed.
Legacy MemberOf versus MemberOf Next
The gap between the two operators is wider than the syntax suggests. Here's how the source material compares them:
| Comparison | Legacy MemberOf Operator | MemberOf Next |
| Availability | Public preview ended November 3, 2026 | Public preview introduced at Microsoft Ignite |
| Processing Architecture | Shared processing with other dynamic membership groups | Separate processing architecture designed for large tenants |
| Tenant-Wide Impact | Could slow down dynamic membership processing across the tenant | Isolated processing prevents impact on other dynamic groups |
| Membership Updates | No predictable dedicated update schedule | Scheduled updates twice a day |
| Group Priority | High (default) | Standard (mandatory) |
| Rule Syntax | MemberOf operator with standalone rule expressions | Same MemberOf syntax |
| Rule Builder | Rule syntax box only | Supports the rule builder |
| Licensing | Microsoft Entra ID P1 | Microsoft Entra ID Governance |
| Tenant-Wide Limit | 500 groups | 1,000 groups, shared with Transitive Reports To |
| Combining Rule Conditions | The memberOf attribute couldn't be combined with other conditions or operators | Can be combined with other supported conditions using the rule syntax editor |
| Cloud Support | Public preview ended | Available only in the Microsoft Entra public cloud; not supported in national clouds |
The licensing row deserves attention. Moving from P1 to Governance changes the cost conversation, not just the configuration one. The table's note on national clouds also matters if any of your tenants sit outside the public cloud, because MemberOf Next won't be available there.
Checking your tenant before the deadline
Start with the inventory. Microsoft Entra doesn't offer a central view of every configuration that depends on memberOf. Dynamic groups, administrative units and entitlement management policies can all use the operator, and checking them by hand gets slow in a large estate.
The source material points to a PowerShell script called MemberOfRuleDeprecationReport.ps1, which scans a tenant and writes separate CSV reports for each supported configuration type. You run it with .\MemberOfRuleDeprecationReport.ps1. It supports interactive sign-in and certificate-based authentication, including unattended runs. By default it scans every supported type. You can limit a run with -DynamicGroups, -AdministrativeUnits or -AutoAssignmentPolicies. Run it in a test or read-only context first, and check the output before acting on it.
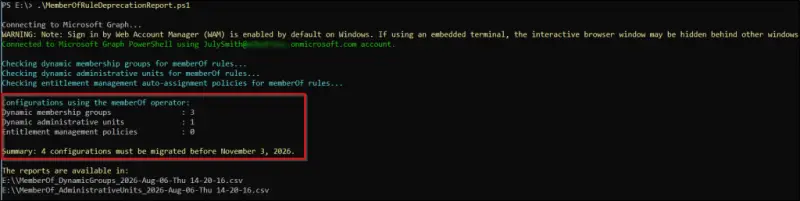
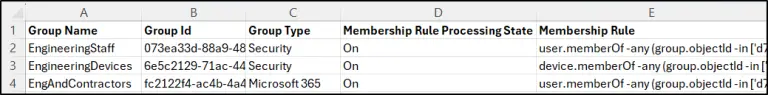
The report sections cover dynamic membership groups and administrative units. Use them as your working list for the migration.
Dynamic Membership Groups:
Administrative Units:

Switching groups to Standard priority
Switching priority is the step that actually moves a group onto the new schedule. The membership rules and existing members stay in place. Before you switch, confirm that every source group referenced in each rule still exists. If one has been deleted, remove its object ID from the rule, or the target group won't update.
For a handful of groups, use the Microsoft Entra admin center. Go to Entra ID > Groups > All groups, select the dynamic membership group, open Properties, set Group priority to Standard, and save. Repeat for each group.
For larger estates, the source offers a Graph call that sets the same property on a single group:
PATCH https://graph.microsoft.com/beta/groups/{group-id}
Content-Type: application/json
{
  "dynamicMembershipPriority": "Standard"
}
The source also includes a bulk approach using Microsoft Graph PowerShell. It requires Microsoft Graph Authentication and Groups modules version 2.41.2 or later, plus the Group.ReadWrite.All permission, and you replace the tenant ID placeholder before running it. The logic finds dynamic membership groups whose rule matches memberOf, sets their priority to Standard, then reads the properties back to confirm. That script writes to every matching group, so I'd review the list it produces and run it against a pilot set first. Don't feed it the whole tenant on the first attempt.
On permissions, the source lists these roles as suitable: Groups Administrator, User Administrator, Intune Administrator (for security groups only), or Global Administrator. Licensing needs Microsoft Entra ID Governance licences covering each unique member user in dynamic groups using MemberOf Next, and each administrator who creates or configures those groups. Licences are counted once per unique user and don't need to be assigned individually.
Transitive Reports To: the new hierarchy operator
Transitive Reports To extends dynamic rules so they follow an entire management chain. The existing manager property checks only the direct reporting line. This operator also picks up indirect reports, which removes the need to build a separate group for each management level or to script the consolidation yourself.
The key behaviours, as the source describes them:
- Full hierarchy coverage. The selected manager and all direct and indirect reports are included, up to 99 levels below the manager.
- Automatic membership updates. When people join, leave or change managers, membership is refreshed at the next scheduled evaluation.
- Extra conditions allowed. You can combine it with other user attributes to narrow the group.
- User-based only. It supports dynamic user groups, not devices.
- Standard priority and twice-daily updates. Groups using it must be set to Standard and update twice a day, not immediately.
- Shared preview limit. It's in public preview and shares the 1,000-group and administrative-unit limit with MemberOf Next.
Creating one is straightforward. In the Microsoft Entra admin center, go to Entra ID > Groups > All groups and select New group. Set the group type to Security or Microsoft 365, then add a name and description. Under Membership type, choose Dynamic User, and set Group priority to Standard. Select Add dynamic query, pick TransitiveReportsTo from the Operator list, and enter the manager's object ID in the Value field. The rule takes this form:
Transitive Reports To {objectID_of_manager}Save the rule, then save the group.
What to do this quarter
Here's my read. The memberOf retirement has a hard end date, and the grace period is limited to Governance customers, so most teams should treat March 31, 2027 as the outer boundary rather than the target. Start with the report. Find the groups, check which source groups have been deleted, confirm the licence position, and decide which groups can switch to Standard priority without breaking an access process that expects immediate changes.
The two new operators look like a better foundation for dynamic membership, but they trade speed for predictability. Twice-daily updates are fine for most joiner, mover and leaver logic. They're a poor fit for emergency access changes. Plan your migration around that tradeoff, keep the 1,000-group ceiling in mind as you go, and expect the governance conversation to move as much as the configuration does.


